Android APK Inspector
Analyze Android APK files directly in your browser. Extract application details, inspect SDK requirements, and identify sensitive permissions.
Drop your APK file here
Drag and drop your Android application file or browse your device.
📱 APK Analysis Results
✓ Analysis CompleteApplication Information
Requested Permissions
How to Check If an APK File Is Safe to Install (Without Uploading)
Are you downloading an Android app or a modded game from a third-party website? While downloading APK files from outside the Google Play Store gives you access to amazing premium features for free, it also comes with severe security risks. Malware, spyware, and hidden trojans are commonly bundled inside unverified packages.
So, how do you verify if a file is clean before putting your personal smartphone data at risk? The safest solution is to analyze its internal configurations before hitting install.
The Risk of Installing Unverified Android Apps
When a developer compiles an Android package, they define explicit access boundaries in a file called the AndroidManifest. If a simple calculator app or a basic helper utility requests absolute access to your SMS registry, microphone, device location, or camera arrays, it is a massive privacy red flag. Malicious scripts often run silently in the background, draining your battery and transmitting sensitive telemetry to unknown offshore servers.
How to Safely Inspect Your Package Internally
Most traditional online virus scanning tools require you to completely upload large installation files to their web hosting networks. This process not only consumes significant portions of your cellular internet data packages but also poses data leakage concerns if the package contains confidential workplace builds.
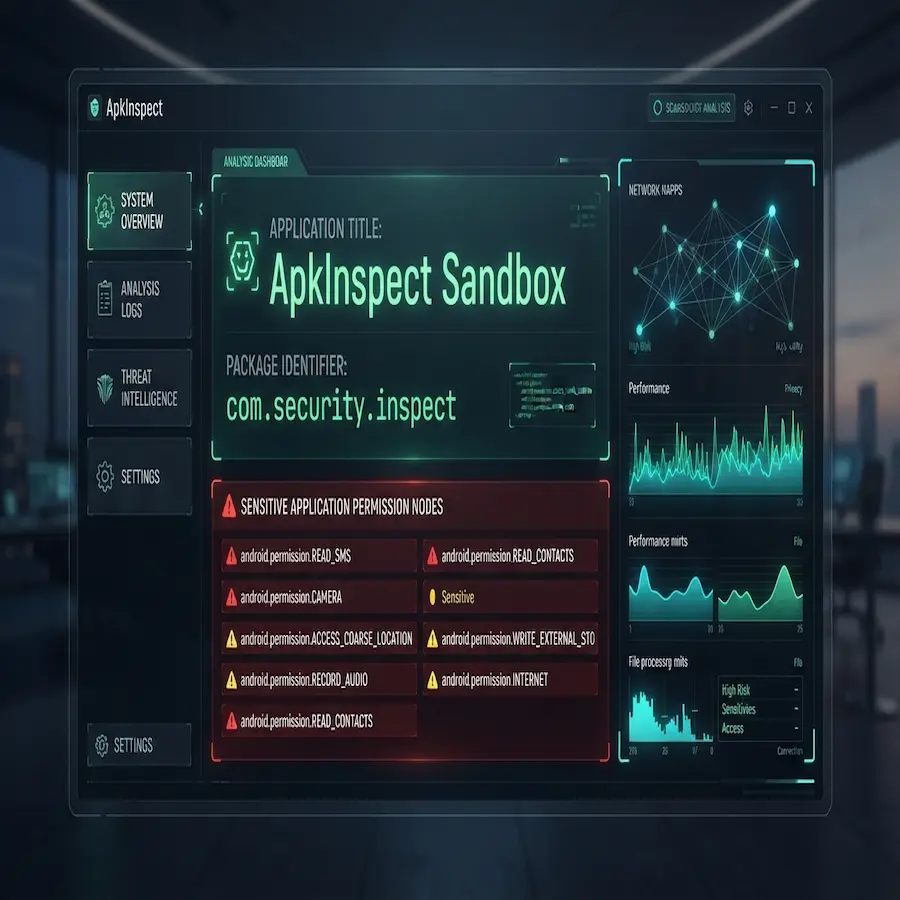
To bypass this network lag, you can use specialized sandbox inspection environments like ApkInspect (https://apkinspect.com/).
Why Use a Client-Side Execution Analyzer?
- Absolute Privacy: The binary unpacking execution layer triggers locally inside your explicit browser container workspace. Your physical installation data never leaves your terminal node.
- Device Fit Metrics: It actively maps compilation nodes to highlight minimal SDK target version limits, preventing boot loops or unexpected runtime framework crashes on newer operating system deployments.
- Instant Permission Mapping: Critical background access points (like background data logging hooks or persistent system overlay permissions) are systematically isolated and flagged red on your screen within milliseconds.
Conclusion
Never blindly install unexpected files on your personal daily driver device. Take thirty seconds to run structural checks through local extraction tools to safeguard your underlying hardware environment against malicious intrusion vectors. Try executing your checkups directly on ApkInspect today!